Friday, March 8, 2024

Learn Java: 94% off Java Programming Certification Kit

Long story short: The 2024 Java Programming Certification Bundle is priced at £19.70, a saving of 94% on the list price.


Java may have been released in 1995, but it remains one of the most popular programming languages ​​due to its flexibility and extensibility, not to mention user-friendliness. Those who wish to switch to a career in software development can choose Java without fear as it eliminates complex syntax. Even those without any coding background will find it easy to learn – but proper guidance is required, of course.

If you want to learn the ins and outs of Java programming, this Java programming certification suite offers seven courses and nearly 90 hours of expert-led instruction. Whether you want to develop a game or build an application for your business, this training is designed to give you the skills to create anything you want using Java. Limited time sale, priced at £19.70.

All seven courses are taught by Packt Publishing, an e-learning provider for IT professionals. No matter your skill level, this training collection will help you become proficient in Java and teach you how to use it to design a variety of digital projects. In addition to theoretical lessons, you can also enjoy practical learning by taking practical tests to test your new skills. You can learn how to write simple and complex programs, create production-ready applications, build APIs, and more. While you gain technical skills, you will also enhance your logical reasoning, critical thinking, and problem-solving skills through these courses.

Mix and match offer

Make 2024 the year you explore careers in tech. You can start learning Java with this training, available for only £19.70.


Source link


from Tech Empire Solutions https://techempiresolutions.com/learn-java-94-off-java-programming-certification-kit/
via https://techempiresolutions.com/

Thursday, March 7, 2024

Sleight of Hand is a neo-noir game from the creators of Framed

Framed Creator Joshua Briggs is back with another mystery game, and this time, it has supernatural elements. RiffRaff Games announces upcoming release gimmicka “third-person card-based mysterious black stealth simulation game” – these words alone make us very interested.

gimmick Lady Luck is a former occult detective who must track down and defeat her former coven. Yes, it’s exciting to see a woman as the noir protagonist who comes to Spire City with a cursed card (which is necessary since she lost her left hand the last time she saw a fellow witch). Each card has a unique ability, such as the Hex card, which can lock onto hidden enemies, and the Hide and Seek card, which can push enemies into view. Another card that sounds useful is called the “Chain Smoker” card: it links the fates of multiple opponents so that Lady Luck can stop them all with one card.

Gameplay also involves solving puzzles to use secret passages and interrogating members of the gathering, all in the hope of finding the leader.all gimmick This is based on a very relevant reason why Lady Luck is putting herself in danger again: She has overdue bills and old debts to pay off. Lady Luck herself is voiced by Debi Mae West, who you may recognize as Meryl Silverburgh from Metal Gear Solid and who is expected to appear in Coming to Steam in 2025 and Game Pass on day one for Xbox Series X|S and Windows PC.

Source link


from Tech Empire Solutions https://techempiresolutions.com/sleight-of-hand-is-a-neo-noir-game-from-the-creators-of-framed/
via https://techempiresolutions.com/

Google follows Apple’s lead and adds new developer fees in EU

Yesterday, Google outlined the changes it will make to comply with the European Union’s Digital Markets Act (DMA) that comes into effect today. However, it leaves out an important detail, which is whether developers who instruct users outside the Play Store to sideload apps will be charged — and if so, how much.

Now, Google has revealed that it does charge developers even if they don’t use the Play Store, just like Apple does with the App Store. According to new details found in the Play Console Help section, the company will be charging two new fees:

  1. There is an initial acquisition fee of 10% for in-app purchases and 5% for a two-year subscription. This represents the value Play provides in facilitating initial user acquisition.

  2. Ongoing service fees are 17% for in-app purchases and 7% for subscriptions. This covers ongoing Play services such as parental controls, security, fraud prevention and app updates.

Developers can opt out of ongoing fees after two years if users agree, but ongoing Play Services will no longer apply. Google said: “Because users purchase the app through Play and expect services such as parental controls, safety scanning, fraud prevention and continuous app updates, discontinuing services also requires user consent.”

Google provides the following chart to show how the fees would apply to a hypothetical “Fantastiq App”:

Google follows Apple's lead and adds new developer fees in EUGoogle follows Apple's lead and adds new developer fees in EU
Google

To this end, Google has taken a similar approach to Apple, reducing App Store commissions but introducing new fees. Namely, Apple is charging a new “payment processing” fee of 3% for transactions made through its store. The new “Core Technology Fee” will charge a flat fee of €0.50 for all app downloads, whether they come from the App Store or a third-party website, after the first 1 million installs.

Google justifies the fees by touting the value it provides within the Android ecosystem: “Fees for Play support our investment in Android and Google Play and reflect the value Android and Play provide, including enabling us to distribute it for free Android and deliver continued growth.” A suite of tools and services that help developers build successful businesses while keeping our platform safe and secure for billions of users around the world. “

Yesterday, Epic CEO Tim Sweeney slammed Google’s post about DMA compliance before the new fees were announced. “Google has announced a malicious compliance plan against Europe’s DMA laws…it looks like their illegal anti-steering policy will be replaced by a new Google tax on online transactions. We may soon find out what he and other developers have to say about this What’s the reaction? New fees.

Source link


from Tech Empire Solutions https://techempiresolutions.com/google-follows-apples-lead-and-adds-new-developer-fees-in-eu/
via https://techempiresolutions.com/

Beware of Spoofed Zoom, Skype, Google Meet Sites Spreading Malware

ReportMarch 7, 2024Editorial DepartmentMalware/cybersecurity

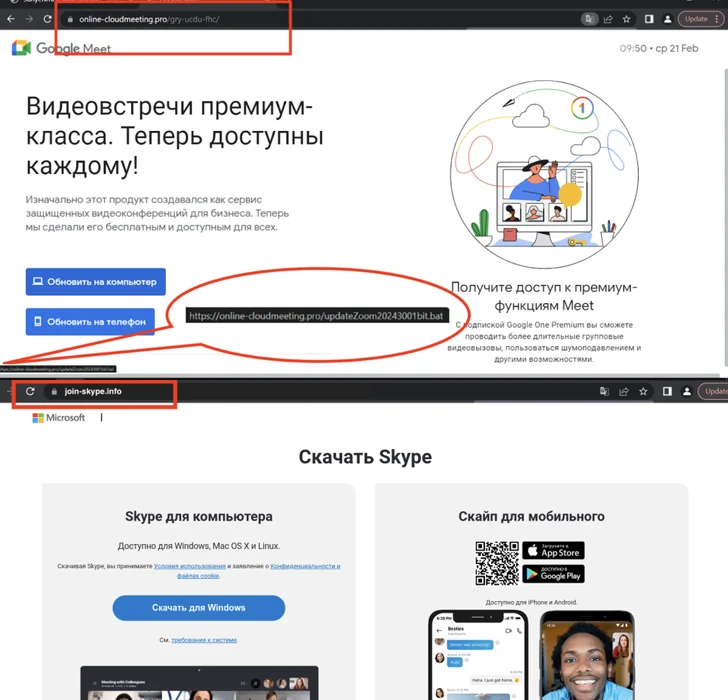
Spoof Zoom, Skype, Google Meet websites

Since December 2023, threat actors have been using fake websites promoting popular video conferencing software such as Google Meet, Skype, and Zoom to spread a variety of malware targeting Android and Windows users.

Zscaler ThreatLabz researchers said: “Threat actors are distributing remote access Trojans (RAT), including SpyNote RAT for Android platforms and NjRAT and DCrat for Windows systems.”

The spoofed websites are in Russian and hosted on domains that are very similar to their legitimate counterparts, suggesting that attackers are using misspelling tricks to lure potential victims into downloading malware.

Internet security

They also provide the option to download the app for Android, iOS and Windows platforms. Clicking the Android button will download the APK file, while clicking the Windows app button will trigger the download of the batch script.

The malicious batch script is responsible for executing a PowerShell script, which in turn downloads and executes a remote access Trojan.

Currently, there is no evidence that the threat actors are targeting iOS users, as clicking the iOS app’s button takes users to Skype’s legitimate Apple App Store listing.

“Threat actors are using these lures to distribute RATs for Android and Windows that can steal confidential information, log keystrokes, and steal files,” the researchers said.

Meanwhile, the AhnLab Security Intelligence Center (ASEC) revealed that a new type of malware called WogRAT targeting Windows and Linux is abusing a free online notepad platform called aNotepad as a hidden carrier to host and retrieve malicious code.

Spoof Zoom, Skype, Google Meet websites

It is said to be active since at least late 2022, targeting Asian countries such as China, Hong Kong, Japan and Singapore. That said, it’s unclear how the malware spread in the wild.

“When WogRAT first runs, it collects basic information about the infected system and sends it to the C&C server,” ASEC said. “The malware then supports executing commands, sending results, downloading files, uploading those files, etc. Order.”

Meanwhile, a massive phishing campaign orchestrated by financially motivated cybercriminal TA4903 was designed to steal enterprise credentials and potentially launch a Business Email Compromise (BEC) attack. The attacker has been active since at least 2019, with activity intensifying after mid-2023.

“TA4903 frequently conducts campaigns to spoof U.S. government entities in order to steal enterprise credentials,” Proofpoint said. “The actor also spoofs organizations across a variety of industries, including construction, finance, healthcare, food and beverage, and more.”

Internet security

The attack chain involves the use of QR codes (also known as quishing) for credential phishing and reliance on the EvilProxy Adversary in the Middle (AiTM) phishing kit to bypass two-factor authentication (2FA) protection.

Once a target’s mailbox is compromised, threat actors search for information related to payments, invoices, and banking information, with the ultimate goal of hijacking existing email threads and committing invoice fraud.

Phishing campaigns also serve as conduits for other malware families such as DarkGate, Agent Tesla, and Remcos RAT, the last of which uses steganographic bait to drop malware onto infected hosts.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/beware-of-spoofed-zoom-skype-google-meet-sites-spreading-malware/
via https://techempiresolutions.com/

Wednesday, March 6, 2024

Best Salesforce Training Package Discount: 91% Off

Long story short: The 2024 Salesforce Platform App Builder Certification Training Bundle is now available for £11.83, saving 91% on the list price.


If you don’t know what Salesforce is, chances are someone in the office does. With more than 150,000 companies around the world, Salesforce remains the leading platform for customer relationship management. Organizations rely on it to track sales leads, organize customer data, automate sales and marketing processes, and more. Due to the platform’s ubiquity in the workplace, many companies are looking for experts who are familiar with the platform. Career opportunities abound in the Salesforce ecosystem, from developers and administrators to architects and marketers.

If you’re keen to explore a career in Salesforce and want to get involved, the 2024 Salesforce Platform Application Builder Certification Training Bundle can help. Ideal for aspiring developers and administrators, it includes expert-led training on Salesforce customization, and for a limited time, you can buy it for £11.83.

This training package contains three courses led by Packt Publishing, the leading e-learning platform for IT professionals. In addition to learning how to use Salesforce, you can expect to gain new skills, including building Salesforce-based applications, integrating chatbots, and building workflow automation programs.

While video lessons are the core of this training package, quizzes and study guides are also provided to retain knowledge. You can even take practical quizzes to practice your newfound development skills.

Mix and match offer

You can access all courses from any device and have the flexibility to study at your own pace and on your own time. After completing these courses, you’ll also receive a certificate of completion that you can use to bolster your resume.

Previously retailing for over £100, you can now buy this Salesforce training package for just £11.83.


Source link


from Tech Empire Solutions https://techempiresolutions.com/best-salesforce-training-package-discount-91-off/
via https://techempiresolutions.com/

GhostSec and Stormous jointly launch ransomware attacks in more than 15 countries

A cybercriminal group called GhostSec is linked to the Golang variant of a ransomware family called “GhostSec” Ghost Locker.

“TheGhostSec and Stormous ransomware groups are teaming up to conduct dual ransomware attacks against various industry verticals in multiple countries,” Cisco Talos researcher Chetan Raghuprasad said in a report shared with The Hacker News.

“GhostLocker and Stormous ransomware have launched a new ransomware-as-a-service (RaaS) program, STMX_GhostLocker, offering various options to their affiliates.”

Attacks launched by the group targeted victims in Cuba, Argentina, Poland, China, Lebanon, Israel, Uzbekistan, India, South Africa, Brazil, Morocco, Qatar, Turkey, Egypt, Vietnam, Thailand, and Indonesia.

Some of the most affected verticals include technology, education, manufacturing, government, transportation, energy, forensics, real estate, and telecommunications.

GhostSec – not to be confused with Ghost Security Group (also known as GhostSec) – is part of the “Big Five” alliance, which also includes ThreatSec, Stormous, Blackforums and SiegedSec.

Internet security

It was founded in August 2023 to “build better unity and connections for everyone in the internet underworld, and expand and grow our work and operations.”

Late last year, the cybercriminal group ventured into ransomware-as-a-service (RaaS) through GhostLocker, offering the service to other actors for $269.99 per month. Soon after, the Stormous ransomware group announced that it would use Python-based ransomware in its attacks.

Talos’ latest findings show that the two groups have joined forces to not only attack a wide range of areas, but also released an updated version of GhostLocker in November 2023 and launched a new RaaS initiative called STMX_GhostLocker in 2024.

Raghuprasad explains: “The new program consists of three categories of services for affiliates: paid services, free services, and another category for individuals who don’t have a plan but just want to sell or publish material on their blog (PYV Serve) .”

STMX_GhostLocker has its own leak site on the dark web, which lists no fewer than six victims from India, Uzbekistan, Indonesia, Poland, Thailand and Argentina.

GhostLocker 2.0 (aka GhostLocker V2) is written in Go and is advertised as being fully effective and providing fast encryption/decryption capabilities. It also comes with a modified ransom note urging victims to contact them within seven days or risk having their stolen data leaked.

The RaaS program also allows affiliates to track their operations, monitor encryption status and payments through a web panel. They are also provided with a builder to configure the locker payload to their liking, including which directories to encrypt and which processes and services to terminate before starting the encryption process.

Once deployed, the ransomware establishes a connection to the command and control (C2) panel and proceeds with the encryption routine, but not before killing defined processes or services and stealing files matching a specific list of extensions.

Internet security

Talos said it discovered two new tools that GhostSec may be using to compromise legitimate websites. “One of them is the ‘GhostSec Deep Scanning Toolset,’ which is used to recursively scan legitimate websites, and the other is a hacking tool called ‘GhostPresser’ that performs cross-site scripting (XSS) attacks,” Raghuprasad said.

The primary purpose of GhostPresser is to compromise WordPress sites, allowing threat actors to change site settings, add new plugins and users, and even install new themes, demonstrating GhostSec’s commitment to growing its arsenal.

“The group themselves claim they use it to attack victims, but we don’t have any way to verify these claims. Ransomware operators could use this tool for a number of reasons,” Talos told The Hacker News.

“Deep scanning tools can be used to find ways into a victim’s network, and GhostPresser tools, in addition to compromising the victim’s website, can also be used to stage payloads for distribution if they don’t want to use the attacker’s infrastructure.”

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/ghostsec-and-stormous-jointly-launch-ransomware-attacks-in-more-than-15-countries/
via https://techempiresolutions.com/

Bob Iger admits Disney strategically ‘killed some projects’

It turns out Warner Bros. isn’t the only studio canceling its own releases.While the extent of the company’s misfortune was not specified batgirl or Coyote and Acmehas been confirmed disney There are also some strategic “kills” done on the project as part of the acquisition plan its profit Get back on track.

We know this because, well, Disney CEO Bob Iger He said so himself. “You have to kill something that you no longer believe in, and that’s not easy in this industry because either you’ve started and you have some sunk costs, or it’s the relationship with your employees or the creative community,” he said today at Morgan Stanley Danley said at an event, quoted in hollywood reporter. “It’s not easy, but you have to make tough decisions. We’ve actually made those tough decisions. We haven’t made it public yet, but we’ve canceled some projects that we didn’t think were strong enough. “

He didn’t reveal any titles, but fans Maybe we can make some guesses.But Egger used to be is careful to note that he “spent a lot of time with the creators, watching these films, giving detailed notes on these films, engaging in a respectful process that resulted in improvements.”

He’s also inevitably asked about “superhero fatigue,” especially with Enthusiasm for the Marvel Cinematic Universe has waned significantly. “A lot of people think it’s audience fatigue; it’s not audience fatigue. They want great movies. If you build it well, they will come,” Iger said, again emphasizing the importance of “excellence and respect” in cultivating The importance of a creative environment. “Focus is really important. We’ve reduced Marvel’s output, both the number of movies and the number of TV shows they’re making, and it’s really become critical, but I feel good about this team. I feel good about the IP we’re making feels good… [and] The track record speaks for itself. “

In fact, the next Marvel movie—the much-anticipated Deadpool and Wolverine— could really help Disney turn a profit; releases July 26.Disney also has it Inverted and Moana sequel On the road, there are kingdom of the planet of the apes.


Want more io9 news?Find out when the latest news is released Miracle, Star Warsand StarCraft Release, what’s next? DC Universe in Movies and TVand everything you need to know about the future doctor who.

Source link


from Tech Empire Solutions https://techempiresolutions.com/bob-iger-admits-disney-strategically-killed-some-projects/
via https://techempiresolutions.com/

Chuzo Login

How to Login to Chuzo Are you having trouble logging into Chuzo? Let’s explore this guide to trouble shoot your problems. Make Sure...