Saturday, January 27, 2024

Working capital usage of growing companies increased by 26%

Of the five regions analyzed in the Growth Enterprise Working Capital Index, North America ranks second, behind Latin America and the Caribbean (LAC). 71% of North American growing businesses had access to working capital solutions in the past 12 months – the third-highest utilization among all five regions in the study, behind Latin America and the Caribbean and Europe . Nearly nine in 10 finance chiefs across the region said these solutions helped their companies secure favorable payment terms for new ventures. Growth companies in North America appear to experience operational efficiency benefits by using external working capital solutions for strategic rather than tactical purposes.
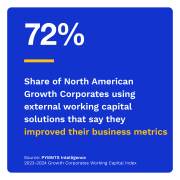
North America’s growing businesses are ready to continue improving operational efficiency through expanded use of working capital solutions. 90% of companies in the region plan to use some type of external working capital solution in the next year, a 26% increase over the past 12 months and the third highest increase.

These are just “Growth Enterprise Working Capital Index 2023-2024: North American Edition“A Pimmts Intelligence and visa cooperate. This version is based on a survey of corporate treasurers or treasurers at what Visa calls growth companies (those with revenues between $50 million and $1 billion). The report examines the working capital solutions that growing businesses can use to raise short-term cash or credit, the preferred uses of these proceeds, and the impact of these solutions on their operating efficiency and business performance.

Other findings from the report include:
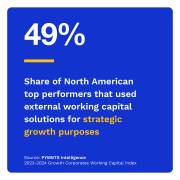
72% of North American growth businesses that leverage external working capital say it improves their business metrics. Nearly nine out of 10 people achieved favorable payment terms for new business initiatives.

Achieving favorable payment terms when trying out new business initiatives was the most cited reason for North American growing businesses using working capital solutions, cited by 87% of respondents.

Outside of the fleet and mobility sectors, North American growth companies tend to use working capital solutions to manage cash flow above average.
Cash flow management enables companies to forecast expenses and develop investment strategies among other key operations, and external working capital solutions are critical in this endeavor. For example, growing businesses in the North American business travel space have high adoption rates of these solutions at 48% for anticipated cash flow gaps, compared to the industry’s global average of 28%. Growing businesses in the North American agriculture sector have the highest usage of working capital solutions for seasonal cash management.

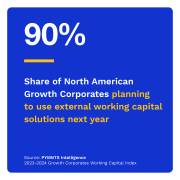
In our study, all of the top-performing growth companies in North America’s fleet and mobility space and seven out of 10 healthcare top performers strategically leverage external working capital to grow and grow their businesses.

A quarter of North America’s top-performing growth businesses use working capital to cover anticipated cash flow gaps; however, North American agriculture and commercial tourism growth businesses use working capital for cash flow continuity reasons at a higher than average rate.

Growth companies in North America have been able to respond to the challenges posed by economic and financial headwinds, demonstrating market resiliency through the use of working capital solutions.Download the report to learn more about how North American growth companies are leveraging working capital solutions.

Source link


from Tech Empire Solutions https://techempiresolutions.com/working-capital-usage-of-growing-companies-increased-by-26/
via https://techempiresolutions.com/

Flipkart co-founder Binny Bansal leaves board

Flipkart co-founder Binny Bansal has resigned from the e-commerce group’s board of directors, two people said on Saturday. The Bengaluru-based startup’s other co-founder, Sachin Bansal, left the board in 2018 after a dispute with investors.

Binny Bansal retains the right to serve on Flipkart’s board for as long as he chooses, citing a conflict of interest with his new venture as the reason for the move. Bansal launched cross-border e-commerce startup OppDoor late last year. According to its website, OppDoor provides end-to-end solutions to businesses, including market entry analysis, demand mapping, inventory management, cross-border logistics and tax assistance.

Prior to this, Bansal sold its entire stake in Flipkart, which was acquired by Walmart for $16 billion in 2018. The e-commerce group has been highly anticipated in recent years and is expected to conduct an IPO in 2025. He currently serves on the Board of Directors of PhonePe and has become a prolific investor in recent years, backing many startups including PhonePe.

“I am proud of what the Flipkart Group has achieved over the past 16 years. Flipkart is in a strong position, with a strong leadership team and a clear path forward, and it is with this confidence that I have decided to resign, knowing that the company is in capable hands. in hand,” Bansal said in a statement.

After leaving Flipkart, Sachin Bansal founded Navi, a financial services company seeking to go public. In 2022, Navi filed documents for an initial public offering but blocked the plan after market conditions deteriorated.

“Flipkart is the result of a great idea and a lot of hard work, built by a team dedicated to changing the way India shops,” Flipkart Group CEO Kalyan Krishnamurthy said in a statement on Saturday. “We wish Binney the best in its future success.” All the best as you embark on your next venture and thank him for the profound impact he will have on the Indian retail ecosystem.”

Source link


from Tech Empire Solutions https://techempiresolutions.com/flipkart-co-founder-binny-bansal-leaves-board/
via https://techempiresolutions.com/

Crackdown on Entrepreneurs | Federal Trade Commission

call them scamEntrepreneur – A marketer who uses hyped promises to sell business opportunities to people who aspire to be their own bosses. As part of a federal and state blitz against counterfeit bizopps, the Federal Trade Commission (FTC) announced the development of seven enforcement actions and five additional cases that the agency says used illegal tactics to steal from 2 million Americans trying to make ends meet. Earned more than $500 million in a challenging economy.

Financial Fraud Enforcement Task Force logoThe Financial Fraud Enforcement Task Force Consumer Protection Task Force’s crackdown also includes 38 criminal actions by the Department of Justice, 15 cease and desist orders by the U.S. Postal Inspection Service, and an additional 20 by state attorneys general in Arizona, California and Colorado. Action, Indiana and Ohio.

The FTC’s actions illustrate a number of questionable business opportunities: mystery shopping services, credit card processing operations, websites purporting to be associated with high-end brands, promoters promising Postal Service jobs, business activities related to mortgage insurance premium refunds , rewards and credit card application processing, and an operation that claims to match companies with excess inventory with businesses looking to buy. But according to the FTC, they all have one thing in common: They all use deceptive tactics to peddle their bizopps.

The new cases coincide with related FTC actions, including a $478 million judgment against John Beck Amazing Profits in August 2012, as well as lawsuits against Infusion Media Inc., AED Inc. and Abili-Staff Ltd. Nearly $6 million was returned to buyers.

The tactics targeted in today’s case are not new — the FTC has a history of challenging counterfeit bizopp — but this time, the agency has a new tool to use against entrepreneurs: the revised Business Opportunity Rule, which requires broad bizopp sellers disclose key information upfront in a streamlined one-page document.

A message to those who aspire to be their own boss: before investing a dime, consult the Federal Trade Commission’s free resources to help you evaluate your existing situation and avoid Bizoop Barracuda.

What do bizopp sellers need to know? First, federal and state partners take bizopp deception seriously. Illegal activity can result in severe restraining orders, multi-million dollar judgments, and jail time. But for sellers eager to avoid law enforcement conflicts, we have information to help them comply with the law more easily. Watch this video to learn more about your obligations under the revised Business Opportunities Rules.

Source link


from Tech Empire Solutions https://techempiresolutions.com/crackdown-on-entrepreneurs-federal-trade-commission/
via https://techempiresolutions.com/
Friday, January 26, 2024

Best Beer Vending Machines 2024 (UK)

Question: Is there anything better than a cold, fresh, relaxing, delicious, proper beer at the bar? Answer (as if we actually needed an answer): Absolutely not.

We also enjoy drinking beer at home – a bag of cans or bottles are fine – but it’s not the same as a pint in the pub. This is why home water dispensers are becoming more and more popular. For beer lovers, a water dispenser should be used along with a coffee machine or a kettle – essential appliances that every kitchen needs.

But where to start? Different drinks meet different needs, and so do beer machines. So we’ve rounded up a range of machines suitable for every kind of beer lover.

How does a beer dispenser work?

It really depends on the brewer you buy. Some use kegs, some use their own technology, and some allow you to pour beer directly. We even have a dispenser that sucks the beer straight from the can and turns it into a pint of real ale. Most models use a keg or a variation of a keg.

How much beer can the brewer hold?

While it would be easier for brands to list keg and water dispenser capacities in pints – that’s how we like to drink, after all – they are measured in liters. Most dispensers can hold a keg of about 5 liters (1.76 pints per liter), but some can hold a little more or less.

What types of beer are used in vending machines?

Being limited to kegs doesn’t mean you’re limited in your choice of beer brands. In fact, there are a wide and growing variety of beer kegs on the market, with brands including Budweiser, Stella Artois, Baker’s, Brewdog, Leffe, Goose Island, Corona and Camden Hells. The Krups machines we’ve included in this roundup use their own style of kegs—oversized tanks called “torps”—and include a few alternative breweries and brands. The range includes Amstel, Moretti, Tiger, Lagunitas and Brixton, among others. Or you can purchase a home brewer that allows you to brew a variety of beers.

How much does a beer dispenser cost?

Luckily, this review of home beer dispensers includes a range of prices, from well under £100 to almost £400. There are cheaper options, but if you want high quality, be prepared to spend at least a few hundred pounds. Keep in mind that kegs also have ongoing costs. A 6-litre bucket costs between £30 and £45, depending on which brand you prefer.

What is the best beer maker for home use?

Like the beer itself, it all comes down to personal taste. Maybe you need something to keep the beer flowing at parties, or maybe you’re a serious beer connoisseur who wants the absolute best machine money can buy and the best-tasting brews. No matter what, there’s something for you on this list. We taste-tested the reviews and scoured the internet for great options for beer lovers of all kinds.

What are the best beer machines of 2024?


Source link


from Tech Empire Solutions https://techempiresolutions.com/best-beer-vending-machines-2024-uk/
via https://techempiresolutions.com/
Microsoft warns that APT29 espionage attacks targeting global organizations are expanding

ReportJanuary 26, 2024Editorial DepartmentThreat Intelligence/Cyber ​​Attacks

APT29 spy attack

Microsoft said Thursday that Russian state-sponsored threat actors launched a cyberattack on its systems in late November 2023. They have been targeting other organizations and are now beginning to notify them.

This development comes just a day after Hewlett Packard Enterprise (HPE) revealed that it had fallen victim to an attack by a hacker group tracked as APT29also known as BlueBravo, Cloaked Ursa, Cozy Bear, Midnight Blizzard (formerly Nobelium), and The Dukes.

“This threat actor is known to primarily target governments, diplomatic entities, non-governmental organizations (NGOs) and IT service providers in the United States and Europe,” Microsoft’s Threat Intelligence Team said in a new advisory.

Internet security

The main goal of these espionage missions is to collect sensitive information of strategic interest to Russia by maintaining a foothold for an extended period of time without attracting any attention.

The latest revelations suggest the event may be larger than previously thought. However, the tech giant did not reveal which other entities were singled out.

APT29’s operations involve using legitimate but compromised accounts to gain and expand access within target environments and fly under the radar. It has also been known to identify and abuse OAuth applications for lateral movement between cloud infrastructure and for post-breach activities such as email harvesting.

“They leverage multiple initial access methods, ranging from credential theft to supply chain attacks, leveraging on-premises environments to move laterally to the cloud, and leveraging the service provider’s chain of trust to gain access to downstream customers,” Microsoft noted.

Another notable tactic is the use of compromised user accounts to create, modify and grant high privileges to OAuth applications, which they can abuse to hide malicious activity. The company notes that this allows threat actors to maintain access to the application even if they lose access to the initially compromised account.

These malicious OAuth applications were ultimately used to authenticate to Microsoft Exchange Online and target Microsoft corporate email accounts to steal data of interest.

Internet security

In a November 2023 incident against Microsoft, threat actors used a password spray attack to successfully infiltrate legacy non-production test tenant accounts that did not have multi-factor authentication (MFA) enabled.

Such attacks are launched from a decentralized residential proxy infrastructure to hide their origin, allowing threat actors to interact with compromised tenants and Exchange Online through a vast network of IP addresses that are also used by legitimate users.

“Due to the high translation rate of IP addresses, Midnight Blizzard uses residential proxies to obfuscate connections, making traditional indicators of compromise (IoC)-based detection unfeasible,” Redmond said. This makes it imperative for organizations to take measures to defend themselves. Malicious OAuth applications and password spraying.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/microsoft-warns-that-apt29-espionage-attacks-targeting-global-organizations-are-expanding/
via https://techempiresolutions.com/

Fortress Heroes is coming to iPhone

Apple is granting more access to its manicured walled gardens to comply with the European Union’s (EU) Digital Markets Act (DMA).in a Press releasethe company announced a raft of upcoming changes to iOS, Safari and the App Store, including support for apps from third-party app stores and the ability to set browser engines other than Safari’s WebKit as the default.

Most of the changes only apply to Apple EU users with Mac and iPhone hardware, such as the ability to use browser apps other than Safari.but there is one feature In particular this will give iPhone More flavor of Android for everyone in the world.Since Apple is opening up iOS to third-party app stores, it will finally allow Third-party game streaming services. Epic celebrated the news by sharing Fortress Heroes on Twitter/X Return to iOS.

Apps such as Nvidia’s GeForce Now and Xbox Game Pass will be available on iPhone. Even better, they will run locally rather than emulated through a mobile browser.You must bring a compatible backbone or Razer Shores controller, if you already wield a controller you’ll probably want this Play games on Apple devices Weird flag.

Streaming games isn’t the only category to get EZ Pass.apple also allowed Application for hosting mini-apps, mini-games, chatbots and other plugins on iOS. They even have access to Apple’s in-app purchase system so you can purchase content. So fun!

Of course, it’s not all red roses in the garden. In a press release, Apple reminds users that without its management, you are at risk. “Inevitably, new options… create new risks for Apple users and their devices,” Apple wrote. The company warned that it “contains scams, fraud, and abuse, or Apps that lure users into contacting illegal, objectionable, or harmful content” do not have much power.

The new rules also angered some people Developer feather. CNBC pointed out that Apple is adopting a new fee structure that will charge developers who do not host the company’s App Store a per-install fee, which may be as high as the typical 30% App Store fee.

Here’s how you can learn about upcoming changes Developer support page.New APIs (approximately 600 of them) are also available in the latest version iOS 17.4 beta. All other features will be rolled out to the 27 EU countries starting in March 2024.


Source link


from Tech Empire Solutions https://techempiresolutions.com/fortress-heroes-is-coming-to-iphone/
via https://techempiresolutions.com/
Thursday, January 25, 2024

New CherryLoader malware mimics CherryTree to deploy PrivEsc vulnerability

ReportJanuary 25, 2024Editorial DepartmentThreat Intelligence/Malware Research

CherryLoader malware

A new Go-based malware loader called cherry loader Discovered by threat hunters in the wild, it can deliver additional payloads to compromised hosts for subsequent exploitation.

Arctic Wolf Labs, which discovered the new attack tool in two recent intrusions, said the loader’s icon and name disguised itself as the legitimate CherryTree note-taking application to trick potential victims into installing it.

Researchers Hady Azzam, Christopher Prest and Steven Campbell said: “CherryLoader was used to remove one of two privilege escalation tools, PrintSpoofer or JuicyPotatoNG. One, then runs a batch file to establish persistence on the victim device.”

In another novel twist, CherryLoader also includes modularization capabilities, allowing threat actors to swap vulnerabilities without recompiling the code.

Internet security

It is unclear how the loader was distributed, but attack chains examined by the cybersecurity firm show CherryLoader (“cherrytree.exe”) and its associated files (“NuxtSharp.Data”, “Spof.Data” and “Juicy”). .Data”).Data”) is contained in a RAR archive file (“Packed.rar”) hosted on IP address 141.11.187[.]70.

Downloaded with the RAR archive is an executable (“main.exe”) that is used to decompress and launch the Golang binary, and it only fires if the first argument passed to it matches the hardcoded MD5 password hash. will continue.

The loader then decrypts “NuxtSharp.Data” and writes its contents to a file on disk named “File.log”, which in turn is designed to use fileless techniques to decode “Spof.Data” into “12. log” and run something called process ghosting, which was first exposed in June 2021.

“The modular design of this technique allows threat actors to replace Spof.Data with other vulnerable code,” the researchers said. “In this case, Juicy.Data containing different vulnerabilities can be used without recompiling File. .log.”

Internet security

The process associated with “12.log” is linked to an open source privilege escalation tool called PrintSpoofer, while “Juicy.Data” is another privilege escalation tool called JuicyPotatoNG.

After successfully elevating privileges, a batch file script named “user.bat” is executed to set persistence on the host and disable Microsoft Defender.

“CherryLoader is [a] The newly discovered multi-stage downloader exploits different encryption methods and other anti-analysis techniques to attempt to detonate alternative, publicly available privilege escalation vulnerabilities without requiring any code to be recompiled. ” the researchers concluded.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/new-cherryloader-malware-mimics-cherrytree-to-deploy-privesc-vulnerability/
via https://techempiresolutions.com/

Chuzo Login

How to Login to Chuzo Are you having trouble logging into Chuzo? Let’s explore this guide to trouble shoot your problems. Make Sure...