Thursday, January 25, 2024

New CherryLoader malware mimics CherryTree to deploy PrivEsc vulnerability

ReportJanuary 25, 2024Editorial DepartmentThreat Intelligence/Malware Research

CherryLoader malware

A new Go-based malware loader called cherry loader Discovered by threat hunters in the wild, it can deliver additional payloads to compromised hosts for subsequent exploitation.

Arctic Wolf Labs, which discovered the new attack tool in two recent intrusions, said the loader’s icon and name disguised itself as the legitimate CherryTree note-taking application to trick potential victims into installing it.

Researchers Hady Azzam, Christopher Prest and Steven Campbell said: “CherryLoader was used to remove one of two privilege escalation tools, PrintSpoofer or JuicyPotatoNG. One, then runs a batch file to establish persistence on the victim device.”

In another novel twist, CherryLoader also includes modularization capabilities, allowing threat actors to swap vulnerabilities without recompiling the code.
Internet security

It is unclear how the loader was distributed, but attack chains examined by the cybersecurity firm show CherryLoader (“cherrytree.exe”) and its associated files (“NuxtSharp.Data”, “Spof.Data” and “Juicy”). .Data”).Data”) is contained in a RAR archive file (“Packed.rar”) hosted on IP address 141.11.187[.]70.

Downloaded with the RAR archive is an executable (“main.exe”) that is used to decompress and launch the Golang binary, and it only fires if the first argument passed to it matches the hardcoded MD5 password hash. will continue.

The loader then decrypts “NuxtSharp.Data” and writes its contents to a file on disk named “File.log”, which in turn is designed to use fileless techniques to decode “Spof.Data” into “12. log” and run something called process ghosting, which was first exposed in June 2021.

“The modular design of this technique allows threat actors to replace Spof.Data with other vulnerable code,” the researchers said. “In this case, Juicy.Data containing different vulnerabilities can be used without recompiling File. .log.”
Internet security

The process associated with “12.log” is linked to an open source privilege escalation tool called PrintSpoofer, while “Juicy.Data” is another privilege escalation tool called JuicyPotatoNG.

After successfully elevating privileges, a batch file script named “user.bat” is executed to set persistence on the host and disable Microsoft Defender.

“CherryLoader is [a] The newly discovered multi-stage downloader exploits different encryption methods and other anti-analysis techniques to attempt to detonate alternative, publicly available privilege escalation vulnerabilities without requiring any code to be recompiled. ” the researchers concluded.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/new-cherryloader-malware-mimics-cherrytree-to-deploy-privesc-vulnerability/
via https://techempiresolutions.com/

Tech giant Hewlett Packard Enterprise was attacked by Russian hackers, related to Democratic National Committee breaches

ReportJanuary 25, 2024Editorial DepartmentCyber ​​attack/data leakage

Russian hackers

Kremlin-linked hackers are suspected of penetrating the cloud email environment of information technology company Hewlett Packard Enterprise (HPE) to steal email data.

“Beginning in May 2023, threat actors accessed and accessed a small number of HPE mailboxes belonging to individuals belonging to our cybersecurity, go-to-market, business units and other functions,” the company said in a U.S. regulatory filing. Stolen data.” Securities and Exchange Commission (SEC).

The intrusion has been attributed to a Russian state-sponsored group called APT29, which has also been tracked by names such as BlueBravo, Cloaked Ursa, Cozy Bear, Midnight Blizzard (formerly Nobelium), and The Dukes.

Days ago, Microsoft suggested that the same threat actor breached its corporate systems in late November 2023, stealing emails and attachments from senior executives in the company’s cybersecurity and legal departments and others.

Internet security

HPE said it was notified of the incident on December 12, 2023, meaning the threat actor persisted undetected in its network for more than six months.

It also noted that the attack may be related to a previous security incident, also attributed to APT29, which involved unauthorized access and exfiltration of a limited number of SharePoint files back in May 2023. It received an alert about malicious activity in June 2023.

However, HPE stressed that the incident has not had any significant impact on its operations so far. The company did not disclose the scale of the attack or the exact email messages that were accessed.

APT29, assessed as part of Russia’s Foreign Intelligence Service (SVR), has been behind a number of high-profile hacks in recent years, including the 2016 attack on the Democratic National Committee and the 2020 breach of the SolarWinds supply chain.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/tech-giant-hewlett-packard-enterprise-was-attacked-by-russian-hackers-related-to-democratic-national-committee-breaches/
via https://techempiresolutions.com/
Wednesday, January 24, 2024

The first bipedal robot arrives at BMW factory

BMW has signed an unprecedented agreement to have “humanoid” robots working at one of its factories. The robots are designed to operate more flexibly than traditional industrial robots and are said to assist luxury carmakers in various parts of the manufacturing process.

The robots, designed by California-based robotics company FigureAI, are described as “universal” robots, meaning they can be used to perform any number of physical tasks. The bipedal robot, simply called “Figure 01,” stands 5 feet, 6 inches tall, weighs 130 pounds, and has five fingers that the company claims can be used to physically construct objects. On its YouTube channel, Figure shows a video of a robot making coffee. Another video shows the robot zipping across a room on its two sturdy legs.

That said, it’s not entirely clear what the robot would actually do in this situation.related Press release Talk of “deploying humanoid robots in automotive manufacturing environments” and claims that the robots will focus on “difficult, unsafe or tedious tasks” all sound rather vague.

The press release further states that as part of the first phase of the deal, the two companies will work together to “identify initial use cases for Figure robots in automotive production.” Again, the wording here makes it sound like neither company has a good idea of ​​what the robots will actually do. After the two companies finally reach an agreement on Figure 01’s capabilities, some of the robots will be deployed at one of BMW’s manufacturing facilities in Spartanburg, South Carolina.

“For decades, single-purpose robotics has saturated the commercial market, but the potential of general-purpose robotics has not been fully exploited,” said Brett Adcock, CEO of Figure. “Figure’s robots will enable companies to increase productivity, reduce costs and create a safer, more consistent environment.”

Figure has been steadily releasing photos and videos of its new hires:

Technology companies around the world are currently racing to produce the first generation of “humanoid” robots. While robots have been functioning in factories and warehouses for years, the new robot’s human form factor is thought to bring many additional benefits to more complex industrial jobs. Of course, this raises concerns that robots will (eventually) take away a lot of human jobs. Figure’s CEO claims that his company has no interest in taking people’s jobs — and, of course, that’s what he says.

Gizmodo reached out to Figure for more details about the deal, and we will update this story if we hear back.

Source link


from Tech Empire Solutions https://techempiresolutions.com/the-first-bipedal-robot-arrives-at-bmw-factory/
via https://techempiresolutions.com/
Patch your GoAnywhere MFT now

ReportJanuary 24, 2024Editorial DepartmentVulnerability/Endpoint Security

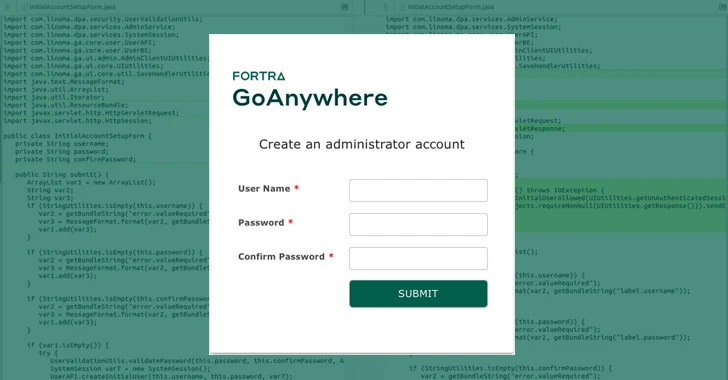
A critical security vulnerability has been disclosed in Fortra’s GoAnywhere managed file transfer (MFT) software that could be abused to create new administrator users.

Tracked as CVE-2024-0204this question has a CVSS score of 9.8 out of 10.

“An authentication bypass in Fortra GoAnywhere MFT prior to 7.4.1 allowed unauthorized users to create administrator users through the admin portal,” Fortra said in an advisory posted on January 22, 2024.

Internet security

Users unable to upgrade to version 7.4.1 can apply a workaround in non-container deployments by deleting the InitialAccountSetup.xhtml file in the installation directory and restarting the service.

For container-deployed instances, it is recommended to replace the archive with an empty archive and restart.

Mohammed Eldeeb and Islam Elrfai of Cairo-based Spark Engineering Consultants are thought to have discovered and reported the flaw in December 2023.

Horizon3.ai, a cybersecurity company, has released a proof-of-concept (PoC) vulnerability for CVE-2024-0204. The company stated that the issue is caused by a path traversal vulnerability in the “/InitialAccountSetup.xhtml” endpoint. The vulnerability can be exploited to create administrative users.

“The simplest indicator of compromise that can be analyzed is any new addition to the admin user group in the GoAnywhere Admin Portal Users -> Admin Users section,” said Horizon3.ai security researcher Zach Hanley.

Internet security

“If the attacker has left this user here, you may be able to observe their last login activity here to estimate the approximate date of the compromise.”

While there is no evidence that CVE-2024-0204 is actively exploited in the wild, last year the Cl0p ransomware group abused another flaw in the same product (CVE-2023-0669, CVSS score: 7.2), resulting in nearly 130 victims attack.

Did you find this article interesting?follow us Twitter and LinkedIn to read more exclusive content from us.


Source link


from Tech Empire Solutions https://techempiresolutions.com/patch-your-goanywhere-mft-now/
via https://techempiresolutions.com/

eBay plans to cut 1,000 jobs because it’s not growing fast enough

E-commerce company eBay said today it plans to lay off 1,000 employees, or about 9% of its workforce, due to current economic conditions. The company said in a blog post that it also plans to cut contract positions in the coming months.

CEO Jamie Iannone acknowledged that the company was hiring quickly but was not growing fast enough to justify the headcount.

“Despite external pressures, such as a challenging macroeconomic environment, we know we can do better through factors within our control. While we have made progress on our strategy, our total headcount and spend have exceeded growth of our business,” Iannone said in a note to employees on Tuesday.

“To address this, we are implementing organizational changes, aligning and integrating certain teams to improve the end-to-end experience and better meet the needs of our customers around the world.”

The company joins Google, Amazon (including Twitch and Audible), Discord, Duolingo, Pixar and Unity, among many other organizations, in announcing layoffs in January 2024.

In the third quarter of 2023, eBay’s revenue was US$2.5 billion and profit was US$1.3 billion. However, the company gave weak fourth-quarter guidance as it sees consumer spending on a downward trajectory. The company also made $2.2 billion last year from selling its stake in online advertising business Adevinta to Permira and Blackstone. In July, the e-commerce company acquired Certilogo, which provides digital IDs for clothing. eBay will report fourth-quarter earnings next month.

The company has been embroiled in some controversy of late. Earlier this month, it agreed to pay $3 million in connection with an online tracking case involving an American couple’s businesses. Last September, the Justice Department accused the e-tailer of selling products that could harm the environment and public health.

Source link


from Tech Empire Solutions https://techempiresolutions.com/ebay-plans-to-cut-1000-jobs-because-its-not-growing-fast-enough/
via https://techempiresolutions.com/

Tuesday, January 23, 2024

The Rise of Virtual Reality: How VR is Changing the Way We Experience Entertainment and Education

Virtual Reality (VR) has been rapidly gaining popularity in recent years, and its impact on the entertainment and education industries is undeniable. From immersive gaming experiences to interactive educational simulations, VR is revolutionizing the way we engage with content. In this article, we will explore the rise of virtual reality and how it is changing the way we experience entertainment and education.

Enhanced Entertainment Experiences

Virtual reality has transformed the entertainment industry by offering new, immersive experiences for consumers. VR allows users to step into a virtual world and interact with their surroundings, creating a sense of presence and realism that traditional media cannot replicate. Whether it’s exploring a virtual museum, attending a live concert, or experiencing a thrilling adventure game, VR provides unparalleled levels of immersion and engagement.

  • Example 1: The video game industry has seen a surge in VR titles, with popular franchises like “Half-Life” and “Resident Evil” offering VR versions of their games.
  • Example 2: VR cinemas have emerged, allowing moviegoers to watch films in a virtual theater with friends from around the world.

Revolutionizing Education

Virtual reality is also making waves in the education sector, providing students with interactive and engaging learning experiences. From exploring distant planets to dissecting virtual frogs, VR allows students to go beyond textbooks and immerse themselves in the subject matter. This hands-on approach to learning has proven to be highly effective in improving student engagement and understanding.

  • Case Study: In a study conducted by Stanford University, students who learned about coral reefs through a VR experience demonstrated a 30% improvement in their understanding compared to those who learned through traditional methods.

Statistics and Growth of VR

According to Statista, the global VR market is projected to reach a value of $40.4 billion by 2025, indicating the rapid growth and adoption of VR technology. In addition, the Entertainment Software Association reported that 21% of U.S. gamers aged 6-64 have tried VR, highlighting the widespread interest in immersive gaming experiences.

Conclusion

As virtual reality continues to evolve and expand its influence, it is clear that VR is changing the way we experience entertainment and education. With its ability to create immersive, engaging experiences, VR is reshaping the entertainment industry and revolutionizing the education sector. Businesses looking to stay ahead in this technological revolution should consider integrating VR into their offerings to stay competitive and meet the growing demand for immersive experiences.

At Tech Empire Solutions, we offer cutting-edge technological solutions to help businesses thrive in the digital age. From VR development to marketing automation, our comprehensive services can elevate your business to new heights. Contact us today to learn how we can help your business succeed in the era of virtual reality.


from Tech Empire Solutions https://techempiresolutions.com/the-rise-of-virtual-reality-how-vr-is-changing-the-way-we-experience-entertainment-and-education/
via https://techempiresolutions.com/

The ‘Mother of Data Breaches’ Has Leaked 26 Billion Records, But Don’t Panic

A database containing 26 billion leak records has been discovered, dubbed the “mother of all leaks.” Luckily, it’s actually not as bad as it sounds.

The massive 12 TB leak was discovered by cybersecurity researcher Bob Dyachenko in collaboration with the Cybernews team. It’s unclear who is responsible for the database, but it contains credentials and sensitive material.

This is undoubtedly bad news. It is never a good thing to have your personal data exposed online as anyone can find it and use it for nefarious purposes. However, the situation is far less catastrophic than it seems.

See also:

As far as we know, the Xfinity data breach affected more than 35 million people

This leak is actually a compilation of information from thousands of previous leaks and does not appear to contain any new information. If you stay up to date on the latest safety information, you should be no more worried than you were yesterday. It is also reasonable to expect that some records are duplicates, so there are not necessarily 26 billion unique records.

Even so, that doesn’t mean you should be complacent. Given the sheer volume of the material and the number of leaks it involves, there’s a good chance your material will be included, even if it’s from a leak you already know about that happened years ago. This is a good reminder to update your security hygiene and maybe change some passwords.

Tencent was the most affected by the breach, with a total of 1.5 billion records included. This was followed by Chinese social media platforms Weibo (504 million), MySpace (260 million), Twitter (281 million) and Wattpad (271 million). Other brands include LinkedIn, AdultFriendFinder, Adobe, MyFitnessPal and Canva.

Government organizations are not immune, with the United States, Brazil, Germany, Turkey and the Philippines included in the compiled database.

You can use tools like Have I Been Pwned or Cybernews’ Breach Checker to find out if you’ve been the victim of a data breach. If you haven’t done so already, consider using a password manager. It may not prevent leaks, but it will make it easier to use unique passwords for all your accounts.


Source link


from Tech Empire Solutions https://techempiresolutions.com/the-mother-of-data-breaches-has-leaked-26-billion-records-but-dont-panic/
via https://techempiresolutions.com/

Chuzo Login

How to Login to Chuzo Are you having trouble logging into Chuzo? Let’s explore this guide to trouble shoot your problems. Make Sure...